TL;DR: Multi-factor authentication (MFA) means proving who you are in more than one way, for example a password plus a code on your phone. The DfE requires MFA for relevant staff and administrator accounts. But the login itself is not what an attacker ultimately wants. A trusted school account can become a route to pupil and staff data, finance systems, genuine email conversations and even parents. Stronger identity protection is about making that route harder to exploit — and spotting it quickly if somebody still gets through.
MFA = multi-factor authentication: an extra check after a password. ‘Phishing-resistant’ means using a sign-in method designed so a fake website cannot easily steal and reuse that extra proof. Identity protection has a second job too: noticing when an account that has signed in successfully starts behaving in a way that does not look normal.
A compromised school account carries trust with it. An attacker may not simply steal files; they can read genuine conversations, learn how the school operates, impersonate staff and send believable requests to people who already trust the sender. In one real school example, parents received a convincing fake email about a ski trip asking for deposits. The risk was not an abstract ‘cyber attack’ — the school’s trusted identity was being used to make fraud look legitimate.
Most of us have used multi-factor authentication, even if we do not call it that.
You enter your password, then approve a notification, type in a code from your phone or use another way to prove it is really you. That is MFA: multi-factor authentication.
It is an important extra layer of security, and the DfE requires it for relevant staff and administrator accounts. But understanding the requirement is only half the conversation. The more useful question is why somebody wants the account in the first place.
What the attacker is actually after
Usually, they are not interested in the pleasure of logging into a school system. The account is a route to something more valuable: data, money, access, or the trust attached to the person whose name is on the email.
That changes how a school should think about phishing. Imagine a member of staff receives an email that looks genuine and follows a link to what appears to be the normal Microsoft sign-in page. They enter their password and then the code from their phone. A sophisticated fake page can sometimes pass those details straight to the real service while the attacker is still connected, allowing the sign-in or session to be hijacked.
To the member of staff, nothing obviously went wrong. To the attacker, however, a trusted identity may now be available to explore.
That trust can be more valuable than the password itself. We’ve seen the consequence in practice: a school was caught out when a fake email was sent to parents about a ski trip and asked them to pay deposits. The message worked because it arrived in a context parents recognised and trusted. That is the ‘why’ behind stronger identity protection — a compromised account can be used to make the next fraudulent request look entirely ordinary.
Making a stolen login harder to use
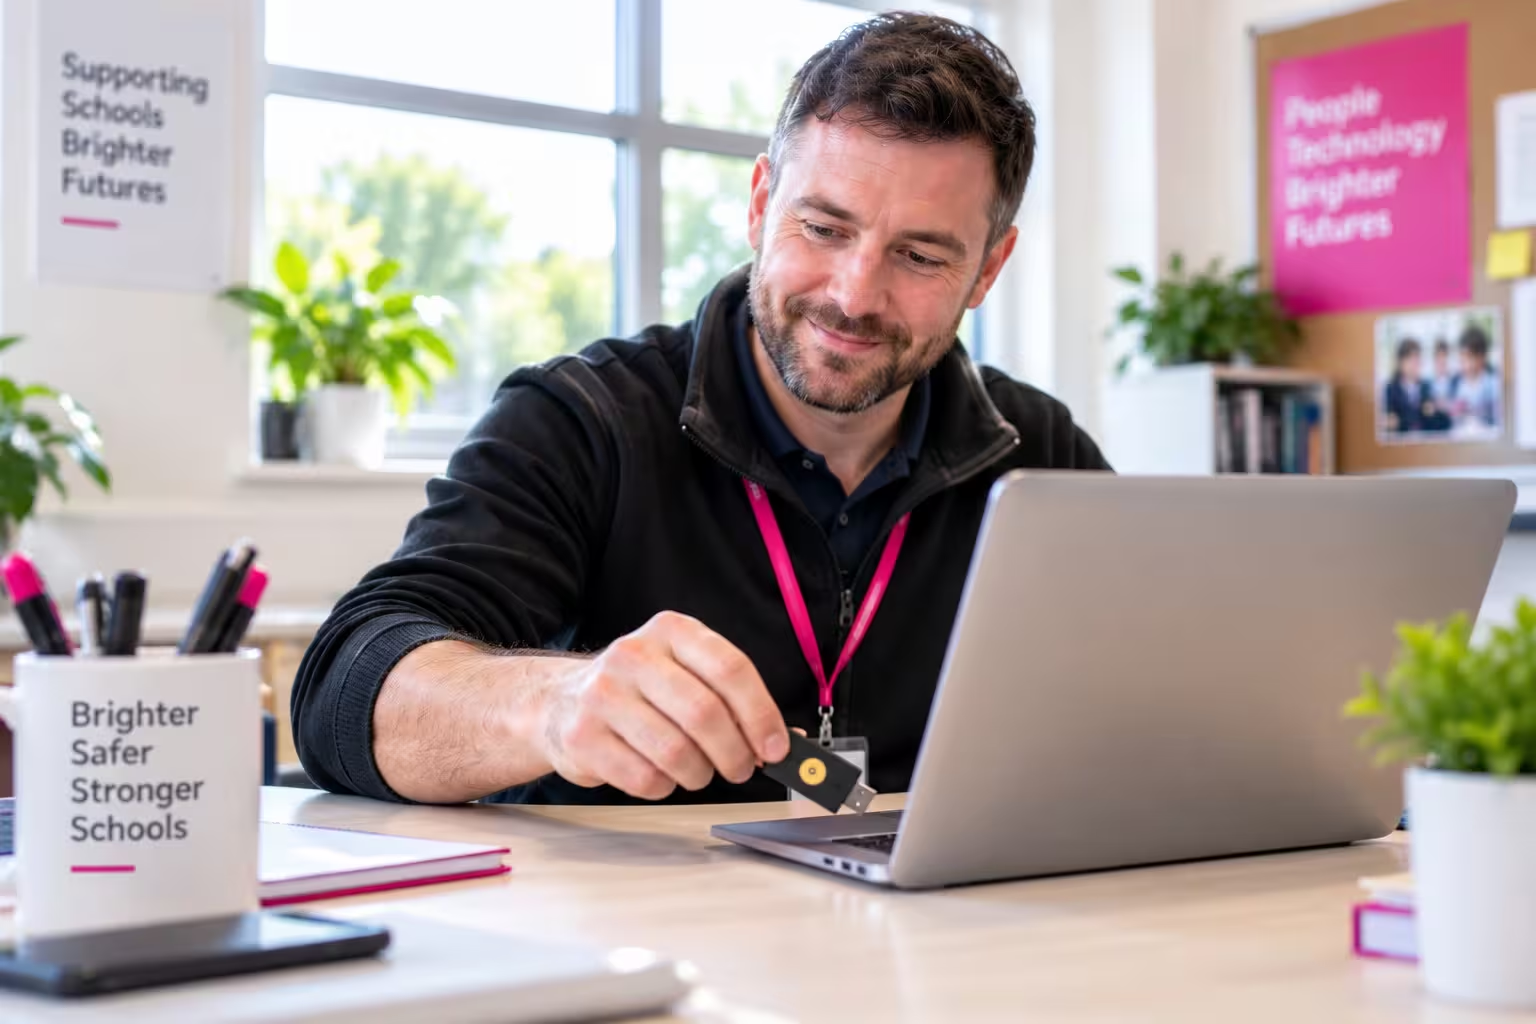
This is why ekte recommends stronger, phishing-resistant sign-in methods for the accounts where compromise would cause the greatest damage. A physical security key or suitable passkey is designed to recognise the genuine service, making it much harder for a fake sign-in page to reuse the login. Finance and IT administration are sensible places to start rather than trying to change every account overnight.
But a stronger front door is not the whole identity story. ekte would also ask whether unusual account activity is being noticed after sign-in, whether older sign-in methods can bypass stronger protection, whether email protection is doing its job and whether important security updates are being applied.
The school does not need to configure all of that itself, and it does not need to become frightened of every email. It needs confidence that the important gaps have been identified, somebody is responsible for them, and the controls around its most valuable accounts are appropriate.
The question worth asking
The useful question for a business manager, headteacher or governor therefore becomes: if somebody managed to use one of our trusted accounts, what could they reach, what could they convincingly do in our name, what would stop them — and how quickly would we know?
Ask your IT support: Which accounts would give an attacker the greatest access to data, money or trusted communications? What type of MFA protects them now? Can the highest-risk accounts use a security key or suitable passkey? Is anything watching for unusual sign-in behaviour after MFA? If an account were compromised, what would happen next and who would be alerted?